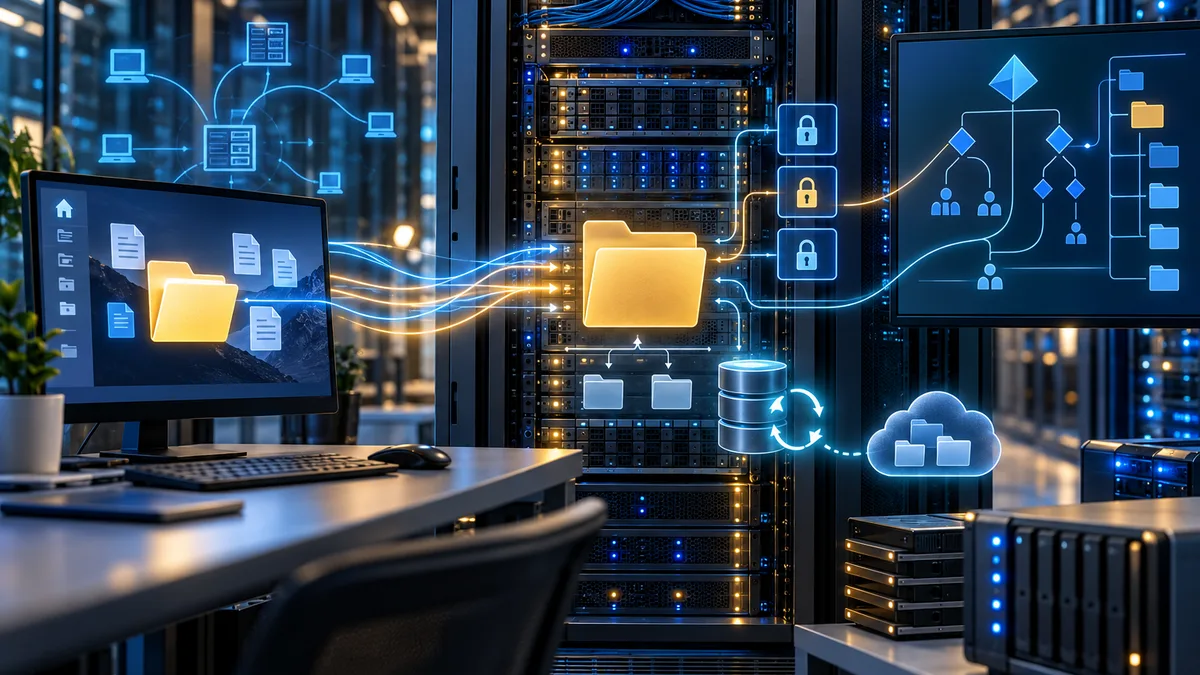
Folder Redirection solves a problem every admin recognizes: users keep important files on their local Desktop and in Documents, those folders never get backed up, and when a laptop dies or a user moves machines, the data is gone. Redirect those folders to a file server and the files live somewhere managed — backed up, available from any domain PC the user signs into, and out of the local profile.
It’s a mature feature and it works well, but the setup has a few sharp edges. Get the share permissions wrong and users either can’t access their own files or can see everyone else’s. Skip Offline Files and your laptop users lose access the moment they leave the building. Redirect AppData carelessly and you can slow logons to a crawl.
This guide walks the whole process: prepare the file share, build the GPO, choose the right redirection options, and handle laptops and migrations without losing data.
How Folder Redirection works
Windows has a set of “known folders” — Documents, Desktop, Pictures, AppData(Roaming), Downloads, and so on. Folder Redirection changes where one or more of these point, from the local profile (C:\Users\<name>\...) to a UNC path on a server (\\fileserver\Redirect\<name>\...).
To the user, nothing looks different. Their Documents folder opens normally; the files just happen to live on the server. Because the data is on the file server, it gets backed up with everything else and follows the user between machines.
Folders worth redirecting (and ones to be careful with)
| Documents | The classic candidate. Redirect it. |
|---|---|
| Desktop | Users dump files here; redirecting it captures them. |
| Pictures / Music / Videos | Often set to follow Documents. |
| AppData (Roaming) | Useful but heavier — large or chatty apps can slow logon. Test first. |
| Downloads | Optional; can be large and low-value. Many skip it. |
Step 1: Prepare the file share
The redirection target is a shared folder on a Windows Server. The permissions are the part to get right, because they decide whether users can reach their own data and stay out of everyone else’s.
Microsoft’s recommended model: create a share, then set permissions so the group of users can create their own subfolder, and each user owns their own redirected folder. You don’t pre-create per-user folders — Windows creates each one and assigns ownership the first time the user’s policy applies.
Recommended share/NTFS permissions (root folder)
| Redirected Folders group | List folder / read data + Create folders (this folder only) |
|---|---|
| Redirected Folders group | Read permissions, traverse — but not full access to subfolders |
| SYSTEM | Full control |
| Administrators | Full control |
| Creator Owner | Full control (subfolders only) — so each user owns their own folder |
# Create and share the folder (adjust path and group as needed)
New-Item -Path "D:\Redirect" -ItemType Directory
New-SmbShare -Name "Redirect" -Path "D:\Redirect" -FullAccess "Domain Admins" `
-ChangeAccess "Domain Users"Step 2: Create the Folder Redirection GPO
Now build the policy.
- In Group Policy Management, create a new GPO and link it to the OU containing your users (Folder Redirection is User Configuration, so it follows the user, not the computer).
- Edit the GPO and go to:
User Configuration
  > Policies
    > Windows Settings
      > Folder Redirection
> Documents (and Desktop, Pictures, etc.)- Right-click Documents > Properties.
- Set Setting to Basic - Redirect everyone’s folder to the same location. (Use Advanced if you want different file shares per security group.)
- Set Target folder location to Create a folder for each user under the root path.
- Enter the root path, e.g.
\\fileserver\Redirect. Windows appends\%USERNAME%\Documentsautomatically.
Step 3: Choose the right options
The Settings tab of each redirected folder has options that change behavior in ways worth understanding.
Folder Redirection settings
| Grant the user exclusive rights | Locks the folder to the user (and SYSTEM). Strong privacy, but admins lose access unless they take ownership. Decide based on your support model. |
|---|---|
| Move the contents to the new location | Copies existing local files into the redirected folder on first apply. Essential for migrating users who already have data. |
| Also apply redirection to Windows 2000/XP | Legacy only — leave off for modern clients. |
| Policy Removal | Choose whether folders move back to the local profile or stay redirected if the GPO no longer applies. |
The two that bite people:
- Grant the user exclusive rights is on by default. If your helpdesk needs to access user files for support, you may want it off (and rely on Creator Owner ownership instead). If you leave it on, admins can’t read the folder without taking ownership.
- Move the contents of [folder] to the new location is what migrates existing data. If you don’t tick it, redirection points to an empty server folder and the user’s old files stay stranded in the local profile.
For the Policy Removal setting, “Redirect the folder back to the local userprofile location when policy is removed” is the safer default — it means removing the GPO doesn’t strand the data on the server.
Step 4: Handle laptops with Offline Files
Redirected folders live on the server, so a laptop off the network can’t reach them — unless you enable Offline Files, which caches a local copy and syncs back when the connection returns.
Offline Files (Client-Side Caching) is enabled by default for redirected folders in many configurations, but confirm it for mobile users. You can control caching behavior through Group Policy under Offline Files settings, including pinning redirected folders for offline availability.
Step 5: Apply and verify
Folder Redirection applies at logon (it’s foreground policy). After creating the GPO:
# On a test client, refresh policy then sign out and back in
gpupdate /force
Have the test user log off and back on — redirection processes during logon, not on a background refresh. Then verify:
# Confirm the Documents known folder now points to the share
[Environment]::GetFolderPath('MyDocuments')

# Check which GPOs applied to the user (run as the user)
gpresult /r /scope:user
The MyDocuments path should now be the UNC location (or its offline-cached path). If redirection didn’t take, confirm the GPO is linked to the user’s OU, the user is in scope, and that there are no general policy problems — Group Policy not applying: causes and fixes covers the usual suspects.
Folder Redirection deployment checklist
- File share created with create-folder + Creator Owner permission model
- GPO linked to the OU containing the target users (User Configuration)
- Root path set so Windows appends %USERNAME% per user
- 'Move the contents to the new location' enabled for existing-data users
- Exclusive-rights and policy-removal options chosen deliberately
- Offline Files enabled and verified for laptops
- Tested with a real user account: log off, log on, confirm paths
- File server backups include the redirection share
A note on profiles
Folder Redirection is often confused with Roaming User Profiles. They’re related but separate: roaming profiles move the entire profile, while redirection moves only specific data folders. For most environments, redirecting Documents, Desktop, and a few others gives you the “data follows the user and is backed up” benefit without the bulk and fragility of full roaming profiles. You can combine them, but start with redirection alone unless you have a specific reason for roaming profiles.
Wrapping up
Folder Redirection is one of the higher-value things Group Policy can do for you: user data ends up on a managed, backed-up file server, and it follows people between machines. The setup itself is short. The parts that decide success are the share permissions (use the create-folder + Creator Owner model, never Everyone), enabling “move the contents” so existing files migrate, and turning on Offline Files for laptops.
Build it for one test user first, confirm the paths and offline access actually work, then roll it out by OU. Done right, it’s quietly reliable — which is exactly what you want from something every user depends on.